DMARC Record Setup: From p=none to p=reject
Set up DMARC in three stages: start with p=none to collect reports, advance to p=quarantine with pct=10, then reach p=reject. Covers record syntax, alignment modes, reading aggregate reports, and the four most common mistakes.
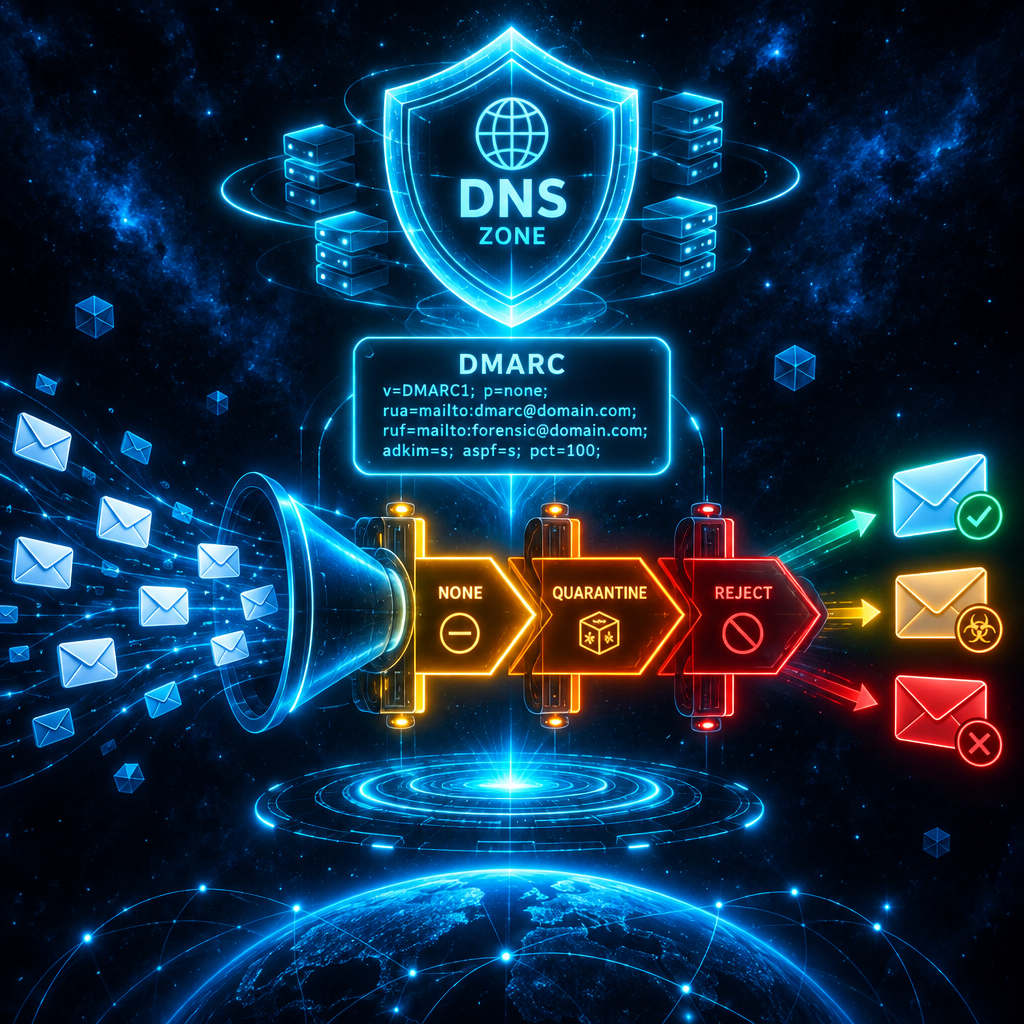
DMARC (Domain-based Message Authentication, Reporting and Conformance) sits on top of SPF and DKIM. It tells receiving mail servers what to do with messages that fail authentication, and it sends you reports so you can see who is sending mail from your domain.
The one-line version
Add a DMARC record to your DNS and start with p=none so you can see what is happening without blocking anything. Read the reports for a week or two. Then tighten the policy.
Record syntax
A minimal DMARC record looks like this:
_dmarc.yourdomain.com. TXT "v=DMARC1; p=none; rua=mailto:dmarc-reports@yourdomain.com"
The important tags:
| Tag | What it does |
|---|---|
v=DMARC1 | Required. Always this value. |
p= | Policy for the domain: none, quarantine, or reject |
sp= | Policy for subdomains. Defaults to the same as p if omitted. |
rua= | Where aggregate reports go (daily digest of all traffic) |
ruf= | Where forensic reports go (individual failure samples, rarely used) |
pct= | Percentage of messages the policy applies to, 1–100. Default is 100. |
adkim= | DKIM alignment: r (relaxed, default) or s (strict) |
aspf= | SPF alignment: r (relaxed, default) or s (strict) |
Relaxed alignment means subdomains count. mail.yourdomain.com satisfies DMARC for yourdomain.com under relaxed alignment. Strict alignment requires an exact domain match.
The three policy stages
Stage 1 — p=none: monitor-only. Failing messages are delivered normally. You receive aggregate reports. Use this to establish a baseline and find all your legitimate sending sources.
Stage 2 — p=quarantine: failing messages go to spam. Use pct=10 to start, watch your reports for a few days, then raise the percentage. Only advance here once your aggregate reports show no unexpected failures from legitimate mail.
Stage 3 — p=reject: failing messages are dropped at the gateway. This is the goal. Once you reach it, spoofing your domain becomes very difficult.
A record for stage 2 at 25%:
"v=DMARC1; p=quarantine; pct=25; rua=mailto:dmarc@yourdomain.com"
Reading aggregate reports
Reports arrive as XML attachments, usually one per sender per day. They look like this in plain terms:
- Source IP:
203.0.113.4, 142 messages - SPF result: pass
- DKIM result: fail
- DMARC disposition: none (policy was p=none)
Most mail providers have a DMARC report viewer that turns the XML into a readable table. Google Postmaster Tools, MXToolbox, and dmarcian all offer free tiers.
Common mistakes
Setting p=reject without monitoring first. If a third-party service like a newsletter tool or ticketing system sends mail from your domain without DKIM, those messages will be dropped. Always start with p=none and give it two weeks.
No rua address. Without reports you are flying blind. Always include it, even on p=none.
Forgetting subdomains. If you have p=reject but no sp= tag, subdomains inherit p=reject by default — which is usually what you want but worth knowing. If you have subdomains that send legitimate mail, check them in your reports before moving to reject.
pct not at 100 when you think it is. The default is 100, so you only need pct= if you want something less. Leaving it at pct=10 and forgetting about it means 90% of failing messages still get through.
Checking your record
dig TXT _dmarc.yourdomain.com +short
You should see your record printed back. If you see nothing, check that the record was saved with the _dmarc. prefix on the right domain.
Further reading: How email authentication works, One-click DNS setup, Why is my email going to spam?