Email OTP security: what to get right
The common security gaps in email OTP implementations — code strength, expiry, rate limiting, constant-time comparison, user enumeration, and logging — and how to address each one.
The common security gaps in email OTP implementations — code strength, expiry, rate limiting, constant-time comparison, user enumeration, and logging — and how to address each one.
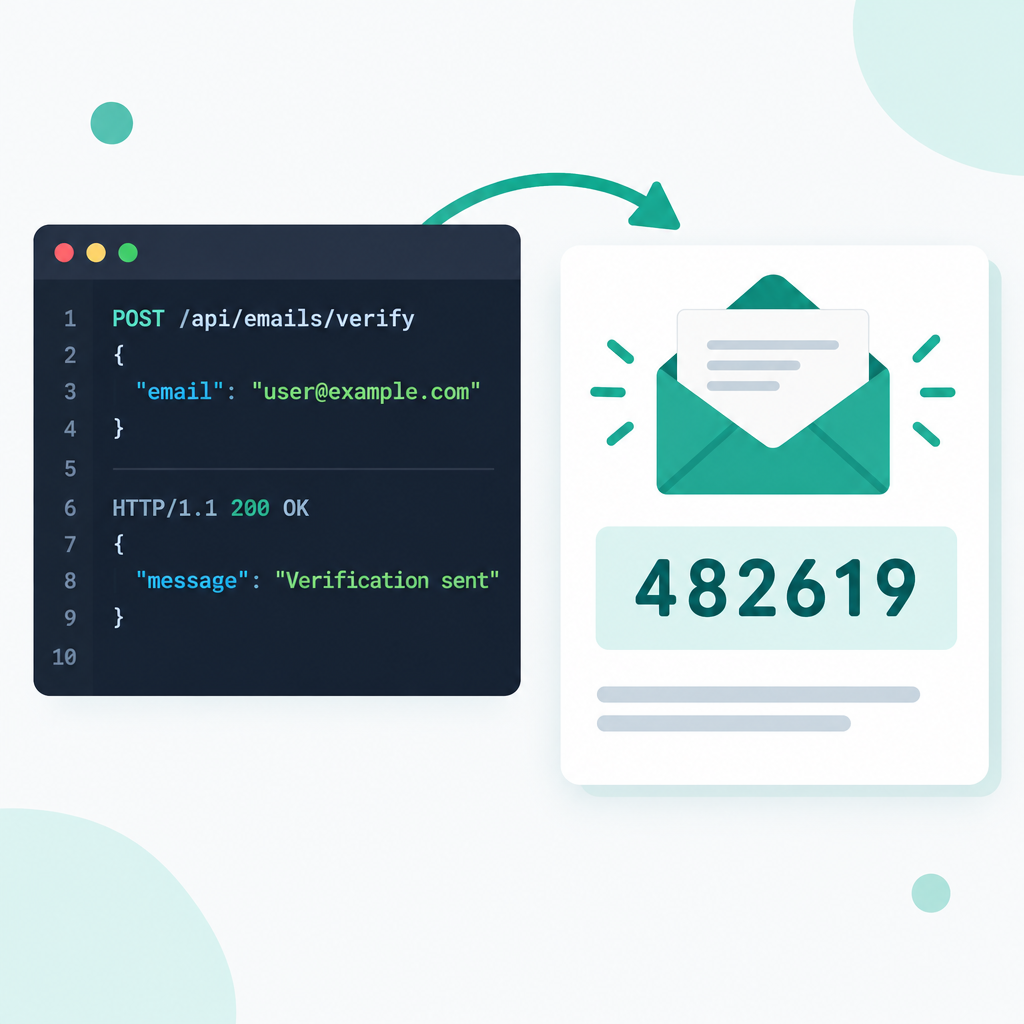
How to send one-time passcodes by email using SMTP or a transactional email API, with code examples for secure random generation, Redis-backed validation, and rate limiting.